Wow! I stared at that thin slab of plastic and thought, huh — this could actually change how people hold crypto. My first impression was skeptical; hardware wallets felt bulky, fiddly, and over-engineered. But something about the smart-card form factor stuck with me. It was tactile, simple, and oddly reassuring in a world of intangible keys and phantom addresses where somethin’ always felt off…
Whoa! The first real test came when I tried to actually use one during a late-night wallet migration. The card was fast. The UX didn’t make me want to throw my laptop. It worked with minimal fuss, which—seriously—is rare. Initially I thought hardware wallets had hit their peak, though actually, wait—let me rephrase that: I assumed there wasn’t much new to invent, but then the card showed me otherwise. My instinct said “this is more user-friendly,” and then the math of backups and key recovery made that instinct stick.
Here’s the thing. For most folks, the problem isn’t cold storage itself. The real headache is backup strategies. People write seed phrases on napkins, store PDFs in cloud folders, or take photos of private keys—sometimes all three. That’s a disaster recipe. On one hand, a written seed is easy to steal or destroy; on the other, digital copies are silently vulnerable to hacks and software bugs. There are trade-offs everywhere, and the best way forward often feels obfuscated by jargon and fear.
Really? Yes. Wallet design has been too focused on a single axis: technical security. That’s necessary, of course. But it’s not sufficient if the average user can’t actually follow best practices without sweating. Let me show you what I mean with a tiny story: I watched a friend lose a three-month-old position because he misplaced a slip of paper during a move. He had a backup…in his messy garage. It was almost comical, except the losses were real. Human behavior matters.
Hmm… thinking about backups quickly spirals into complexity. You can split seeds, use Shamir backup, or rely on multisig arrangements across devices. Those are powerful tools, though they demand discipline and setup time—two things many people avoid. There are tradeoffs between convenience and robustness, and smart-card hardware wallets try to thread that needle by offering a portable, simple, and tamper-resistant key store. They make the “carry one thing” approach feasible for many users.
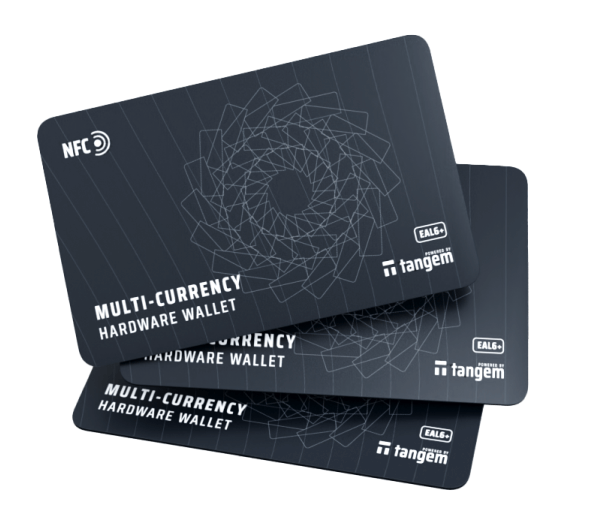
Why the smart-card form factor works (and where it doesn’t)
Short answer: form factor matters. Cards slide neatly into a wallet, they don’t look like expensive tech, and they’re easy to hide in plain sight. I liked that immediately. They’re less “security appliance” and more “everyday object,” which reduces both the intimidation factor and the theft profile. That said, nothing is perfect. Cards can be lost, can demagnetize if you stick them next to a magnet (some will survive, some won’t), and they depend on companion software to sign transactions, so ecosystem compatibility is important.
Okay, so check this out—when I first used a smart-card wallet I expected rough edges. Instead I found streamlined flows and fewer steps than some dedicated dongles. My internal checklist—durability, offline signing, ease of backup—got checked off quicker than usual. On the other hand, I also noticed small UX inconsistencies across mobile apps that pair with these cards, which can trip up non-technical users. That part bugs me.
I’ll be honest: I’m biased toward low-friction security. I’m not 100% sure every power user will love a card as their primary device, but for newcomers and people who want a “set it and nearly forget it” solution, it’s attractive. The card encourages one major behavioral improvement: people protect one physical object rather than a scattered collection of notes and files. That consolidation reduces human error, which is very very important.
Initially I thought private-key protection was a purely technical challenge, but then I realized it’s also a behavioral design problem. Actually, wait—let me put that another way: you can engineer perfect key storage, yet still lose assets if everyday habits aren’t addressed. So design that blends security with real-life routines wins more often than the most impenetrable fortress. On that front, smart-card hardware wallets earn points.
Check this out—if you’re the sort of person who misplaces a USB drive, the card is a better bet. If you tend to forget PINs, though, the card’s small interface can be a downside unless the companion app does a good job. In other words, they remove some failure modes while introducing others, and understanding those tradeoffs is the practical work of securing crypto for the long haul.
Around backups: practical strategies that don’t suck
Backing up private keys should be boring. Seriously. When it’s exciting, you’re doing it wrong. The goal is to reduce variance in outcomes. My recommended approach combines redundancy, geographic distribution, and ease-of-use. Use a primary smart-card wallet for daily or cold storage. Create at least two independent backups that live in separate physically secure locations (a safe deposit box, a trusted relative’s secure place, etc.).
Hmm… a lot of folks skip the redundancy step because it sounds scary. They think “I only need one copy.” That logic fails when faced with fire, theft, or human forgetfulness. So here’s a practical compromise: make a minimalist paper backup of the seed, laminate it, and store it in a secure place, while also keeping a redundant hardware backup (a second card or another certified hardware device). That way, you avoid single points of failure without drowning in complexity.
On one hand, cryptography gives us robust primitives; on the other, human error is still the leading cause of lost funds. The technical solution? Use devices that keep private keys off-network, sign transactions offline, and provide verifiable recovery options. The user-facing solution? Make it easy to follow a repeatable backup drill. Build a habit. Practice recovery once (do a test restore) so you’re not surprised later. Trust grows when process beats panic.
Whoa! For people who are concerned about privacy and physical theft, consider splitting backups using threshold schemes. Shamir-like splits can be great, but they complicate recovery. I recommend them for users who understand the stakes and have reliable custodial locations for shares. For most people, one card plus one geographically separate backup and a laminated paper seed is a realistic and resilient plan.
How I evaluate smart-card hardware wallets
Security first: Is the seed generated on-device? Are keys non-exportable? Does the card resist physical tampering? These matter. Integration next: does the card work with popular wallets and custody services? Usability later: are flows clear for non-experts? My instinct ranks these in that priority order, but usability nudges into the top three for mainstream adoption—because otherwise people create workarounds that defeat security.
Here’s what bugs me about many wallet reviews: they focus on specs and ignore everyday failure modes. An attack vector on paper is not the same as an attack vector on a card. Users need mental models they can actually follow. So when I test a card, I run these scenarios: loss and recovery, battery or device unavailability (if the card needs a phone), accidental damage, and app compromise. If a product fails gracefully under those tests, I take it seriously.
Okay, so if you’re shopping, look for tamper-evident hardware, open-source firmware (or audited closed-source with public audits), and clear recovery instructions that don’t assume expert-level knowledge. Also check whether the maker has a transparent support channel and a clear policy around firmware updates. These are small signals, but they matter a lot over the long term.
One natural recommendation I keep returning to is the tangem wallet approach because it neatly packages many of these traits into a compact smart-card device that integrates well with common wallets and emphasizes private-key protection without excessive friction. If you want a place to start learning more, check out the tangem wallet for concrete examples of how the card model works in practice—it’s not perfect, but it demonstrates the principle well.
FAQ
How is a smart-card wallet different from a USB hardware wallet?
Cards are slimmer, often more discreet, and designed for everyday carry. USB devices can have larger interfaces or require special drivers. Functionally both can keep keys offline, but cards prioritize low-profile form factor and often better social engineering resistance because they look like ordinary items.
What’s the best backup approach for beginners?
Use a primary card and one independent backup stored in a separate secure location. Make a physical paper copy of the seed, laminate it, and test a recovery once. If you’re comfortable, add a second hardware backup or use a threshold split for higher security. Practice the recovery; that single step separates theory from real-world readiness.